Sample report
A report your clients will actually read
These are the opening pages of a real OpenVAS report, generated by Panoptic Scans against scanme.nmap.org, the host the Nmap project keeps online for testing scanners. Your logo goes on the cover. Before the technical findings begin, a plain-English narrative walks the reader through how an attacker would use them.
Your brand on the cover
White-label reports carry your logo, not ours, so MSPs and consultants can hand them straight to clients. ACME Corporation stands in for you here.
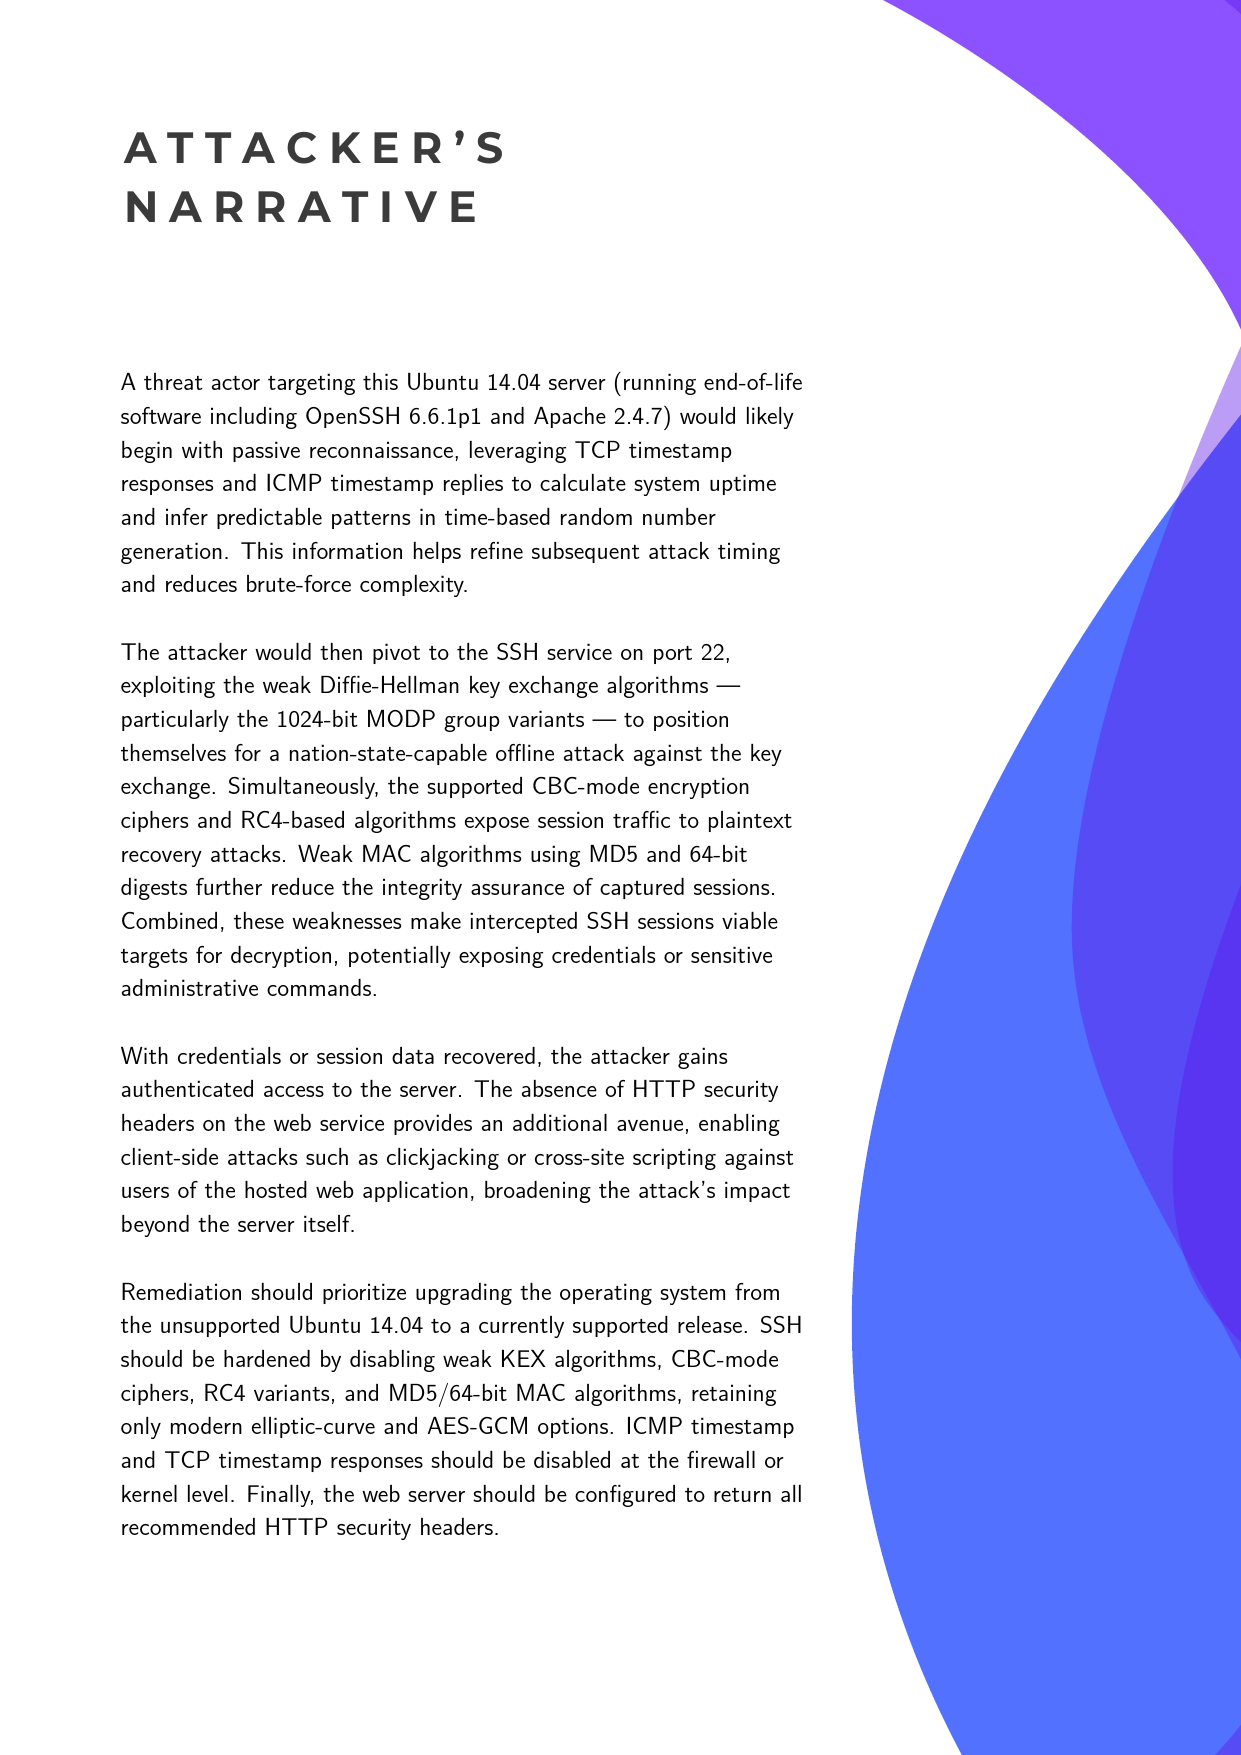
The attacker's narrative
One page that connects the dots: how an attacker would move from reconnaissance to access using these specific findings, and what to fix first. It is the page executives read and engineers act on.
What follows in the full report
The remaining 26 pages hold the evidence behind the narrative. This scan produced 25 results across the host's IPv4 and IPv6 addresses, each listed with its port, CVSS score, detection method, quality-of-detection rating, recommended fix, and references, so an engineer or auditor can verify every claim without logging in.
Attack narratives and white-label branding are included on Premium and Pro. Compare plans
Scan a URL, IP, or hostname
Enter a target and an email address. We'll send a findings report.