Vulnerability Scanning vs Penetration Testing for Indie SaaS: What You Need and When Written on . Posted in Informational.
Sooner or later every indie SaaS founder hears the same two questions. A prospect's security team asks, "When was your last penetration test?" and your SOC 2 auditor asks, "How do you identify vulnerabilities in your environment?" They sound like the same question. They are not, and confusing them is one of the most common ways small teams either overspend on security or leave real gaps open.
This guide explains the difference between vulnerability scanning and penetration testing, what each one actually costs a small team, what auditors and enterprise buyers really look for, and a practical way to combine them at the right stage of growth.
What Is Vulnerability Scanning?
Vulnerability scanning is automated testing that checks your systems against a large, constantly updated library of known weaknesses. A scanner probes your hosts, ports, services, and web applications and reports things like outdated software with known CVEs, exposed admin panels, weak TLS configurations, missing security headers, and common web flaws such as injection or cross-site scripting.
For a SaaS company, scanning usually covers three layers:
- External network scanning - everything reachable from the internet: load balancers, API gateways, mail servers, forgotten staging hosts, and open ports.
- Internal network scanning - the private side of your cloud: databases, caches, worker nodes, and admin tools that should never be exposed but still need patching. See our guide to internal network vulnerability scanning for indie SaaS.
- Web application and API scanning - dynamic testing of your running app, ideally while logged in. Our post on authenticated web application vulnerability scans shows why the logged-in view matters.
The key strengths of scanning are breadth, speed, and repeatability. It runs on a schedule, it does not get tired, and it catches the new CVE that was published last Tuesday against the library you deployed last month.
What Is Penetration Testing?
A penetration test is a time-boxed engagement where a skilled human tester (often assisted by tools) tries to break into your application the way a real attacker would. Instead of checking a list of known issues, a pentester looks for chains: a minor information leak plus a weak password reset flow plus a missing authorization check that together let one customer read another customer's data.
Good pentests follow a recognized methodology such as the OWASP Web Security Testing Guide or NIST SP 800-115, and they end with a written report that ranks findings and explains how each was exploited. That report is a point-in-time snapshot: it describes your security on the days the tester worked, not the week after your next big release.
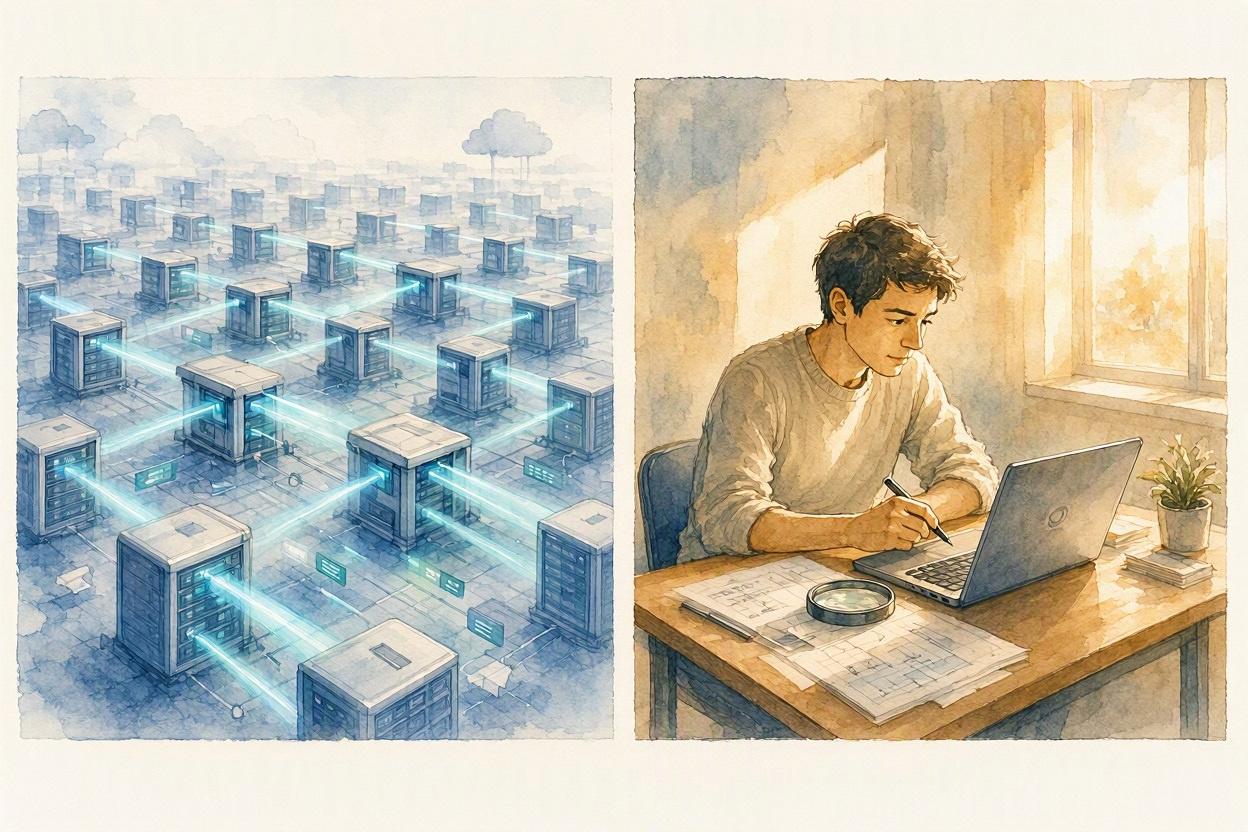
Scanning vs Pentesting: Side-by-Side
| Factor | Vulnerability Scanning | Penetration Testing |
|---|---|---|
| Who does it | Automated tools | Human security testers |
| Frequency | Continuous, daily, or weekly | Usually once a year or after major changes |
| Coverage | Broad - every host, port, and app you register | Deep - a defined scope over a few days or weeks |
| Finds | Known CVEs, misconfigurations, common web flaws | Business logic flaws, chained exploits, authorization bugs |
| Typical cost | Low monthly subscription | Often several thousand dollars or more per engagement |
| Time to results | Minutes to hours | Weeks, including scheduling and reporting |
| Best evidence for | Ongoing control operation in SOC 2 | Customer security reviews and annual assurance |
The Real Cost for a Small Team
For an indie founder, the bigger cost of a pentest is often not the invoice. It is the calendar. You need to define scope, set up test accounts, freeze or at least stabilize the release you want tested, answer the tester's questions, and then fix and retest the findings. A first pentest can easily eat a couple of weeks of founder attention.
Scanning flips that model. Setup is usually a matter of adding your domains, IPs, and app login, then choosing a schedule. After that, the main ongoing cost is triage: reviewing new findings and fixing the ones that matter. If you are new to triage, our guide on vulnerability prioritization for SaaS covers how to separate real risk from noise.
What SOC 2 Auditors and Enterprise Buyers Actually Ask For
The AICPA SOC 2 framework does not name a specific tool or require a pentest by name. Its Trust Services Criteria expect you to identify and evaluate vulnerabilities and to show that your monitoring controls actually operate over the audit period. In practice, auditors most often look for:
- Evidence of regular vulnerability scanning across your production environment, with dated reports.
- A defined process for reviewing findings and remediating them within reasonable timeframes.
- Some form of independent testing, which many auditors and most enterprise customers interpret as a penetration test, typically annually.
That first point is where scanning shines. A Type II audit covers months of operation, and a single pentest report cannot prove that your controls worked continuously across that window. Recurring scan reports can. For a deeper walkthrough, read vulnerability scanning for SOC 2 compliance.
Enterprise security questionnaires tend to ask both questions directly: "Do you perform regular vulnerability scans?" and "Do you conduct annual third-party penetration tests?" Answering yes to the first early on buys you credibility while you budget for the second.
A Practical Plan by Growth Stage
Pre-revenue to first customers
Start continuous external network scanning and authenticated web application scanning as soon as you have anything in production. This is cheap, fast to set up, and catches the most common ways small SaaS products get compromised: exposed services, outdated components, and basic web flaws. A hosted service like Panoptic Scans lets you do this without running your own scanner infrastructure.
Preparing for SOC 2 or first enterprise deals
Add internal network scanning and API coverage, keep a steady weekly or daily schedule, and document how you triage and fix findings. Keep the reports. They become the evidence your auditor asks for and the attachment your prospect's security team wants to see.
Scaling and selling upmarket
Commission your first third-party penetration test once your core product is relatively stable, ideally after scanning has already cleaned up the easy findings. You will pay for the tester's time to find deep, logic-level issues instead of outdated libraries a scanner would have flagged for a fraction of the cost. After that, repeat the pentest annually or after major architectural changes, while scanning keeps running in between.
Why You Need Both, in the Right Order
Penetration testing and vulnerability scanning are not competitors. Scanning is your always-on smoke detector, and a pentest is the periodic inspection by an expert. Running a pentest without continuous scanning means paying a human to find problems a tool could have caught, then going blind until next year. Running scanning without ever pentesting leaves logic flaws undiscovered and enterprise questionnaires half answered.
For most indie SaaS teams, the right order is simple: scan continuously from day one, fix what attackers are most likely to exploit, and add a pentest when customers or auditors start asking for it. If you want to get the first part running this week, create a Panoptic Scans account and set up your first external, internal, and web application scans.